Author: <span>ssl_admin</span>

Uncategorized

The AI/ML Framework for Smart Networks and Services White…

This white paper presents a comprehensive vision for the evolution of smart network infrastructures and services, positioning Artificial Intelligence (AI) as a foundational enabler of sixth generation networks (6G) and next-generation digital ecosystems. Serving as a sequel of the SNWG white paper on AI and Machine Learning (ML) landscape for smart network and services, this white paper highlights the great AI potential for the 6G networks as well as the key challenges emerge from the adoption of AI in network operations. With inputs from multiple SNS JU projects, AI/ML frameworks are presented towards transforming network operations from traditional rule-based management into autonomous, adaptive, resilient, and intent-driven systems. In the service and resource orchestration domain, those frameworks bring intent-driven solutions and enable zero-touch closed loops; while they facilitate orchestration in multi-domain and federated environments. In the application domain, AI/MLenabled applications drive innovation in future network services, including concepts, such as programmability, joint communication & sensing, and Network Digital Twins(NDTs). Regardless of the scope of application and the target network domain where AI/ML is adopted, security, trust and privacy aspects should be considered both for the integral operation of AI/ML components and their lifecycle management. Especially for lifecycle of AI/ML models there is an increased need for pipelines that ensure reproducibility, traceability, continuous learning, and operational consistency.

Find more information: https://smart-networks.europa.eu/wp-content/uploads/2026/08/snwg_ai.ml_frameworks_whitepaperb_final_.pdf 

Uncategorized

Deliverable 3.3 is now available

This document is the deliverable of WP3 – D3.3: User-centric Distributed 6G Core. This deliverable provides a technical documentation of the user-centric distributed 5G/6G core, detailing the implementation details, as well as providing the software components needed for validating the SAFE6G solution with the Metaverse use cases. Specifically, D3.3 describes the technologies, modules and interfaces that are part of the 6G core design as part of the SAFE-6G system to provide the expected trustworthy-related features. This entails the core, and the Metaverse modules that will be used to construct the use cases to validate the SAFE-6G system. Thus, the document defines how all building blocks of the SAFE-6G packet core architecture are integrated together to deliver 6G core to support Metaverse use cases.

Find more information here: https://safe-6g.eu/wp-content/uploads/2026/09/D3.3_SAFE-6G_V1.0.pdf 

Uncategorized

SAFE-6G Releases D3.5

Within the SAFE-6G architecture, the MLOps platform supports the preparation, training and deployment of Machine Learning models used by several key project components, including the SAFE-6G Chatbot, Cognitive Coordinator and AI-powered Trust Functions.

The platform provides an integrated environment covering the AI/ML lifecycle through several complementary capabilities: a Pipeline Development Environment for experimentation and model development, a Pipeline Orchestration Platform for automated ML workflows, Model Storage for datasets and trained models, Model Serving for real-time inference, and a Differential Privacy module for privacy-preserving Machine Learning.

Built around cloud-native technologies and Kubernetes, the SAFE-6G MLOps environment supports traceable model management, systematic versioning and automated deployment. This makes it possible for project partners to move AI models from experimentation to operational execution while maintaining consistency and reproducibility across different environments. One of the important developments described in D3.5 is the Model Serving component, designed within SAFE-6G to bridge the gap between Machine Learning development and operational deployment.

Trained AI/ML models can be packaged into Docker images and Helm charts and deployed automatically in Kubernetes environments. The platform uses technologies including KServe, GitLab CI/CD and Meta-OS integration to create a controlled pathway from trained model artefacts to production-ready inference services.

Model versioning also provides traceability, allowing SAFE-6G components to identify the exact version of a deployed model and, where required, redeploy previous versions in a reproducible manner.

This approach helps simplify the operational side of AI deployment, enabling developers to concentrate on model development while the platform supports the processes required to move models towards real-world use. 

Within the SAFE-6G architecture, the MLOps platform supports the preparation, training and deployment of Machine Learning models used by several key project components, including the SAFE-6G Chatbot, Cognitive Coordinator and AI-powered Trust Functions.

The platform provides an integrated environment covering the AI/ML lifecycle through several complementary capabilities: a Pipeline Development Environment for experimentation and model development, a Pipeline Orchestration Platform for automated ML workflows, Model Storage for datasets and trained models, Model Serving for real-time inference, and a Differential Privacy module for privacy-preserving Machine Learning.

Built around cloud-native technologies and Kubernetes, the SAFE-6G MLOps environment supports traceable model management, systematic versioning and automated deployment. This makes it possible for project partners to move AI models from experimentation to operational execution while maintaining consistency and reproducibility across different environments. One of the important developments described in D3.5 is the Model Serving component, designed within SAFE-6G to bridge the gap between Machine Learning development and operational deployment. Trained AI/ML models can be packaged into Docker images and Helm charts and deployed automatically in Kubernetes environments. The platform uses technologies including KServe, GitLab CI/CD and Meta-OS integration to create a controlled pathway from trained model artefacts to production-ready inference services.

Model versioning also provides traceability, allowing SAFE-6G components to identify the exact version of a deployed model and, where required, redeploy previous versions in a reproducible manner. This approach helps simplify the operational side of AI deployment, enabling developers to concentrate on model development while the platform supports the processes required to move models towards real-world use.

Find it online: https://safe-6g.eu/wp-content/uploads/2026/09/D3.5_SAFE-6G_V1.0.pdf
Uncategorized
SNS JU Annual Activity Report 2025 Highlights Europe’s Progress…

As part of this broader European ecosystem, SAFE-6G – A Smart and Adaptive Framework for Enhancing Trust in 6G Networks – is included within the SNS JU project portfolio.

The Annual Activity Report records 35 publications associated with SAFE-6G, including eight peer-reviewed publications, demonstrating the project’s growing contribution to European research and knowledge creation around future communication networks.

SAFE-6G contributes to the SNS JU vision by investigating how trustworthiness, security and user-centricity can be embedded into future 6G systems, complementing the programme’s broader ambition to ensure that European connectivity technologies are not only technologically advanced but also secure, sustainable and aligned with European values.

Strengthening Europe’s leadership in 6G

Beyond individual projects, the report demonstrates the increasing scale and maturity of the European 6G ecosystem.

The SNS JU continues to combine research, experimentation, standardisation, stakeholder cooperation and international visibility to strengthen Europe’s position in future connectivity. Its activities are designed not only to advance technology but also to reinforce European digital sovereignty, industrial competitiveness and the transition towards secure and sustainable digital infrastructures.

With 20 newly selected projects preparing to join the programme and further funding initiatives already planned, the results presented in the SNS JU Annual Activity Report 2025 provide a strong foundation for the next phase of Europe’s journey towards 6G.

For SAFE-6G, the report also demonstrates how its research forms part of a much wider European effort to build the technologies, architectures and trust mechanisms that will help shape the next generation of connectivity.

Find more information here: https://smart-networks.europa.eu/the-sns-ju-has-released-its-annual-activity-report-2025/ 

Uncategorized

SAFE-6G Deliverable 3.3

The SAFE-6G project has released Deliverable D3.3, “User-centric Distributed 6G Core,” presenting the final technical developments of the project’s distributed 5G/6G core infrastructure.

The deliverable documents how the different technologies, modules and interfaces of the SAFE-6G packet core have been brought together to support the project’s vision of trustworthy, user-centric 6G services, including the infrastructure required for validation through the SAFE-6G Metaverse use cases.

A central objective of the work has been to evolve the traditional 5G Core towards a more distributed, cloud-native and programmable architecture capable of supporting future 6G functionality. Among the implemented developments are containerised signalling and user-plane components, Kubernetes-compatible deployment, interfaces for AI/ML integration through the Network Data Analytics Function (NWDAF), enhanced Network Exposure Function (NEF) capabilities and support for multiple User Plane Function configurations.

An important aspect of D3.3 is the implementation of SAFE-6G across both commercial and open-source core network environments. Alongside the Cumucore platform, the project uses and extends Open5GS, enabling the SAFE-6G architecture to be evaluated in an open and standards-compliant environment. This approach demonstrates that the project’s trust mechanisms, AI-driven functionality and network exposure capabilities are not tied to a single vendor implementation.

SAFE-6G has also developed two key APIs through the Open5GS Network Exposure Function: the NEF Monitoring Event API, which enables authorised applications and trust components to securely access network monitoring information, and the NEF AsSessionWithQoS API, which allows applications to request specific Quality of Service requirements for individual application sessions.

The open-source implementation, documentation and deployment resources for these APIs have also been made available through the SAFE-6G software repositories, supporting further experimentation and reuse.

Overall, D3.3 marks an important step in SAFE-6G’s transition from 5G core capabilities towards an AI-enabled, distributed and interoperable 6G core architecture. The final implementation across both Cumucore and Open5GS strengthens portability and interoperability while providing the network foundation needed for the project’s trust-aware services and future validation activities.

Find it online: https://safe-6g.eu/wp-content/uploads/2026/09/D3.3_SAFE-6G_V1.0.pdf

Uncategorized

SAFE- 6G Deliverable 3.4

SAFE-6G has released Deliverable D3.4, “Infrastructure Openness, Monitoring and Programmability,” presenting the final software developments that enable applications and SAFE-6G trust components to securely interact with the project’s underlying network, edge-cloud and Metaverse infrastructure.

The deliverable reports the final outcomes of Task 3.3, bringing together the interfaces and software components developed to expose network capabilities through standardised and project-specific APIs. These interfaces connect the user-centric 5G/6G Core, Edge-Cloud Continuum and Metaverse platform, creating a common foundation for monitoring, infrastructure control and programmable service operation.

At the network level, SAFE-6G provides APIs for both the Cumucore and Open5GS core implementations. These allow authorised components to retrieve monitoring information, interact with network configuration and securely access network capabilities. The Open5GS implementation additionally exposes project-specific NEF functionality while preserving the principles of the 3GPP Service-Based Architecture. 

D3.4 extends this openness beyond the network core. APIs developed for the Edge-Cloud Continuum provide access to orchestration, context and monitoring capabilities, while interfaces for the Metaverse platform enable interaction with immersive applications, digital twins and XR services. The deliverable reports, for example, an XR monitoring capability able to retrieve 92 performance metrics through integration with the CloudXR client environment.

A particularly important outcome is the integration of OpenCAPIF as SAFE-6G’s common API exposure framework. Through OpenCAPIF, services can be securely registered, discovered and accessed across different infrastructure domains. SAFE-6G has further developed the Open Network Exposure Function (O-NEF), which provides an abstraction layer between standardised API exposure and network-specific functionality. Significantly, the O-NEF extension has already been approved by ETSI SDG OCF for inclusion as a new module in a future OpenCAPIF release.

Together, these developments establish a secure, interoperable and standards-based interface through which the SAFE-6G Cognitive Coordinator, Trust Functions and authorised applications can discover and interact with services throughout the infrastructure.

Find it online:  https://safe-6g.eu/wp-content/uploads/2026/09/D3.4_SAFE-6G_V1.0.pdf

Uncategorized

Open Community Experience (OCX) 2026

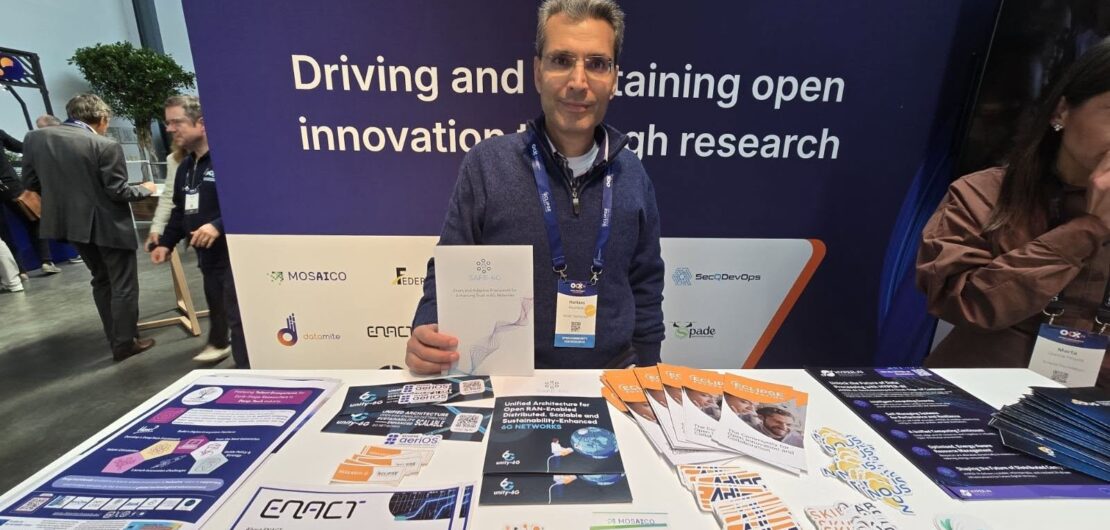
The Open Community Experience (OCX) 2026 is the Eclipse Foundation’s flagship open-source conference, bringing together developers, researchers, industry leaders, policymakers, and EU-funded projects to explore the latest advancements in open-source technologies. Held in Brussels, the event features dedicated tracks on AI, cloud and edge computing, automotive, compliance, developer tooling, and research, fostering collaboration between academia, industry, and open-source communities. As a key platform for showcasing innovative European research, OCX 2026 highlights how open-source ecosystems accelerate the development of secure, interoperable, and trustworthy digital technologies. SAFE-6G’s presence at the Eclipse booth demonstrates the project’s commitment to leveraging Eclipse aeriOS and open-source innovation to advance resilient, secure, and trustworthy 6G systems while strengthening collaboration across Europe’s research and innovation landscape.

Uncategorized

Deliverable 3.6: Metaverse use-cases development and user-centric configuration 

This document belongs to the second round of WP3 deliverables. In contrast to the first round where one single document contained the report of all WP tasks, now each of them has produced their own deliverable. Specifically, D3.6: Metaverse use-cases development and user-centric configuration, reports the final outcomes (mostly software) of Task 3.5. This Metaverse ecosystem comprises the implementation of two major types of components. First, the Unity use-case applications, namely the factory digital twin for UC1 and the XR formation in UC2. And second, the Metaverse manager, which makes the link between the Unity apps and the rest of the SAFE-6G architecture. Besides, this document also presents the final development and integration efforts related to the SAFE-6G Chatbot. All these components have been iterated on during the project and reached their final versions. They are thus ready for the verification and validation activities being performed in WP5. Find it online here: https://safe-6g.eu/wp-content/uploads/2026/07/D3.6_SAFE-6G_V1.0.pdf

Uncategorized

SMEs’ Role in European Innovation: Framework Recommendations to Enable…

Europe is entering the design phase of the 10th Framework Programme (FP10). The choices made now, namely funding rates, eligibility conditions, governance representation, evaluation criteria, and consortium rules, will shape European research and innovation (R&I) for the next decade. For Small and Medium-sized Enterprises (SMEs), these choices are not operational details: they determine whether SMEs remain peripheral participants in European R&I or become central actors of Europe’s technological capacity. This Position Paper is the contribution of the NetworldEurope SME Working Group (WG) to that design phase. Its added value lies in translating aggregated SME experience into a structured, policy-oriented perspective that directly informs the design parameters of FP10. Find more information here: https://www.networldeurope.eu/smes-role-in-european-innovation-framework-recommendations-to-enable-better-sme-contributions-in-fp10/

Uncategorized

Deliverable 3.2: Cloud continuum, service mesh and resource orchestration

This document represents the final software outcomes and architectural implementations of Task 3.1, reporting on the design, execution, and deployment of the Edge-Cloud continuum layer as well as the DataOps module for the SAFE-6G framework. The involved components compose the overall framework that manages distributed computing resources and orchestrates the lifecycle of  microservices across heterogeneous domains, also monitoring their status and performance. At the core of the continuum implementation is a Meta-Operating System based on ECLIPSE aeriOS. This system offers a programmable environment designed to integrate seamlessly with standard Cloud Native technologies. It successfully enables the federation of delocalized computing domains  and provides continuous observability, identity management, and distributed service orchestration using Kubernetes as its foundation. The Meta-OS relies on critical components including a FIWARE  Orion-LD Context Broker for sharing context data without replication, and an enhanced dual-level  orchestration engine to automate the deployment, upgrade, and removal of services packaged as  Helm charts or containers. The flexibility of its data model has allowed the extension of its default  definition with SAFE-6G specific entities and attributes. Also, the exposure capabilities of the 
continuum have been secured by an API Gateway built on KrakenD, fully integrated with OpenCAPIF  Release 3 to facilitate automated API discoverability, access management, and interaction with the broader SAFE-6G Trust Functions. Find more: https://safe-6g.eu/wp-content/uploads/2026/07/D3.2_SAFE-6G_V1.0.pdf